Preserve choice through open foundations, modular architecture, and interoperability, adapting the platform to the mission.
About XaasIO
We’re building a
once-in-a-generation company for critical infrastructure.
XaasIO builds air-gapped, hyperscaler-class cloud platforms for the systems that move money, run cities, connect industry, and protect essential services.
Defining Air-Gapped Full-Stack Cloud for Critical Infrastructure.
Sovereign Cloud Ready
Air-Gapped Ready
Open foundations
No mandatory SaaS control
Why we exist
Critical infrastructure
deserves a
cloud of its own.
We believe modernization should expand what organizations can do without reducing their authority over how they operate. The ability to adopt cloud, data, and AI should not depend on surrendering control of essential systems.
For us, sovereignty means more than the location of data. It means authority over infrastructure, administration, identity, security policies, software changes, and recovery. That conviction shapes the company we are building.
Our mission
To build air-gapped, hyperscaler-class platforms that give critical-infrastructure operators the cloud capabilities they need-and the operational independence
their responsibilities demand.
Our vision
A world where essential services can modernize, scale, and adopt AI while retaining authority over their infrastructure, data, and future.
Convictions behind the company
The Tao of XaasIO
Capability without surrendering control.
Our Tao is the philosophy behind how we build, operate, and evolve XaasIO. One conviction connects every principle: technology should increase capability without diminishing control.
Flexible.
Reliable.
Engineer for continuity through resilient design, tested recovery, and disciplined lifecycle operations.
Secure.
Keep authority within the customer’s trust boundary through isolation, least privilege, controlled change, and auditable operations.
01
Sovereignty is operational control.
Keep authority with the organization responsible for the mission. Design for customer control of infrastructure, administrative access, identities, keys, data, and operational policies, not data residency alone.
02
Air gaps are designed end to end.
Treat disconnected operation as an architectural requirement. Plan for local dependencies, controlled software imports, and operation without a mandatory external SaaS control plane. Validate the complete lifecycle, not just an offline installation.
03
Open foundations. Accountable engineering.
Build on upstream open source and open interfaces. Respect licenses, make dependencies visible, and take responsibility for integration, release quality, documentation, and support.
04
Resilience must be demonstrated.
Design for failure, then test recovery. Favor observable behavior, rehearsed restoration, and validated maintenance procedures over promises that a system will never fail.
05
Automation must remain governable.
Automate repeatable work without removing accountability. Use policy, least privilege, approval boundaries, and audit trails so that operators remain responsible for consequential actions.
06
Intelligence belongs inside the trust boundary.
For disconnected AI, design the model, data, retrieval, inference, and observability paths to operate locally. Keep the use of sensitive information within the customer’s approved environment.
07
Integration must preserve choice.
Build a coherent platform without making every component inseparable. Favor modular services, supported infrastructure options, and documented interfaces so organizations can evolve without unnecessary disruption.
08
Engineer for the full lifecycle.
Treat upgrades, security updates, software provenance, recovery, and support as product concerns. Build for years of operation, not only the first successful deployment.
Open in foundation. Independent in operation. Accountable by design.
What we build
The full-stack cloud.
Inside your control.
We bring infrastructure, cloud operations, data, and AI together as an integrated platform portfolio.
Infrastructure
OpenStack cloud, KVM virtualization, Kubernetes, and storage integration. Build on supported compute, networking, and storage, including Ceph or compatible enterprise storage architectures.
Cloud operations
Bring together cloud management, self-service, identity, automation, and observability. Add metering, service catalogs, and billing where the operating model calls for them.
Data foundations
Create a foundation for managed databases, streaming, analytics, and lakehouse workloads, with access and operations governed inside the approved environment.
Private AI
Deploy private model inference, retrieval-augmented generation, and agent workflows on customer-controlled infrastructure, with the dependencies required for disconnected operation validated in scope.
Full stack means the cloud foundation and its operating layers, not ownership of every industry application. Customers and partners bring the specialized applications, operational systems, and domain expertise.
* Air-Gapped Ready and Sovereign Cloud Ready describe deployment-specific readiness. No mandatory SaaS control plane applies to the validated disconnected scope. Hardware, components, licensing, integrations, and lifecycle dependencies must be assessed before deployment.
Where we focus
Built for systems
where the stakes are real.
Our engineering focus spans critical infrastructure, public-sector organizations, service providers, and sensitive digital platforms where continuity, privacy, and operational control are fundamental.
01 / FOCUS
Banking, Finance &
Insurance
Private cloud foundations for core banking, lending, insurance, risk analytics, and financial-service applications, designed around workload isolation, data governance, resilience, and operational control.
02 / FOCUS
Financial backbones & financial clouds
Cloud foundations for banking, payment, clearing, settlement, and shared financial-service environments where continuity, segregation, and operational governance are central.
03 / FOCUS
Financial Exchanges & Matching Engines
Cloud infrastructure for financial exchanges and order-matching engines, designed around workload-specific requirements for predictable latency, high transaction throughput, resilience, and operational control.
04 / FOCUS
Public Sector Government & Federal
Sovereign cloud foundations for government departments, federal agencies, public-sector organizations, and digital citizen services. Designed around data sovereignty, workload isolation, controlled access, auditability, and continuity of essential public services, with air-gapped deployment options for restricted environments.
05 / FOCUS
Pharmaceuticals
Cloud foundations for pharmaceutical research, manufacturing applications, laboratory systems, and quality-management platforms, designed around data integrity, controlled access, traceability, and application-validation requirements.
06 / FOCUS
Critical Healthcare
Private cloud infrastructure for hospital information systems, clinical applications, medical imaging, and healthcare analytics, designed around sensitive-data protection, workload segregation, resilience, and continuity of essential services.
07 / FOCUS
Oil & Gas
Edge and data-center cloud platforms for upstream, midstream, and downstream operations, including asset monitoring, industrial telemetry, operational analytics, and private AI, with architectures shaped around IT/OT separation and remote-site requirements.
08 / FOCUS
Power Transmission & Grid Infrastructure
Cloud foundations for power-transmission backbones and grid infrastructure, including transmission-asset monitoring, substation data platforms, grid analytics, and operational support applications. Designed around resilience, IT/OT separation, controlled access, and continuity across data centers and remote sites.
09 / FOCUS
Critical Industrial IoT
Edge and core infrastructure for industrial telemetry, asset intelligence, and operational analytics, designed around the separation and availability needs of industrial environments.
10 / FOCUS
Smart cities
Cloud foundations for city operations, video management, mobility services, and urban analytics, with controlled access and local data governance.
11 / FOCUS
Metros & rail
networks
Infrastructure for transport operations applications, station systems, asset monitoring, and passenger-service platforms, with continuity designed around operational requirements.
12 / FOCUS
Defense & electronic warfare systems
Controlled cloud environments for authorized defense workloads, electronic warfare support applications, simulation, and mission-data processing.
13 / FOCUS
Autonomous cyber defense platforms
Infrastructure for defensive security analytics and policy-governed detection and response, with bounded automation, auditability, and human oversight.
14 / FOCUS
MSPs & CSPs
Full-stack cloud platforms for managed service providers (MSPs) and cloud service providers (CSPs) delivering private, sovereign, and customer-dedicated cloud services. Designed around tenant isolation, self-service provisioning, metering, billing, and lifecycle automation, with air-gapped options for customer environments requiring disconnected operation.
15 / FOCUS
Air-gapped AI inference
Locally operated model serving, retrieval, and agent workflows for sensitive information and restricted environments, without mandatory public AI API dependencies in the validated scope.
XaasIO provides the infrastructure foundation. Regulated, safety-critical, real-time, and specialized defense applications require workload-specific architecture, validation, and any applicable approvals.
Our approach to open source
Open foundations.
Long-term freedom.
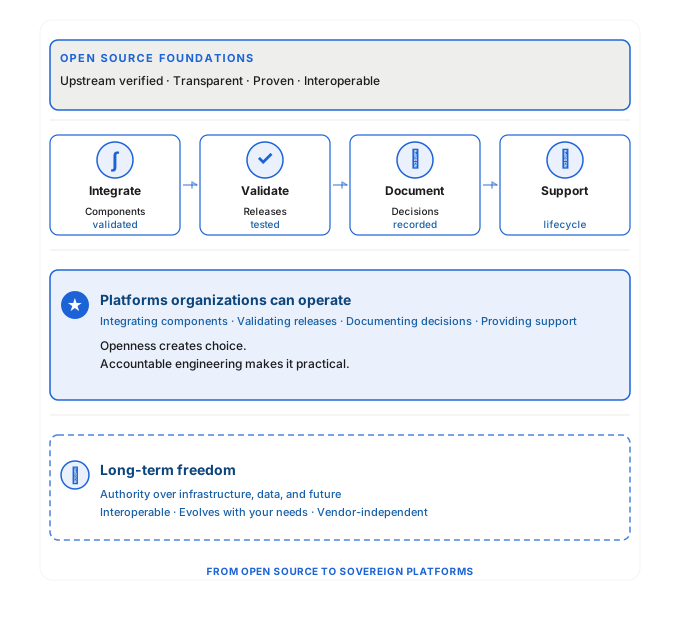
We believe the infrastructure behind essential services should be understandable, interoperable, and able to evolve. Open-source foundations and open interfaces are central to that belief.
Our role is to turn those foundations into platforms organizations can operate: integrating components, validating releases, documenting decisions, and providing enterprise support and lifecycle services. Openness creates choice. Accountable engineering makes that choice practical.
How we engineer
Proven open source.
Engineered for governed
autonomy.
XaasIO focuses on repackaging, hardening, integrating, and extending proven upstream open-source
platforms-engineering them for SOC 2-aligned controls, AI-native capabilities, and autonomous
Day-2 application and platform operations with human governance.
01 / ENGINEERING FOCUS
Proven upstream.
XaasIO engineered.
Start from proven upstream releases. Apply reviewed changes, security testing, and reproducible packaging, with upstream and XaasIO software bills of materials, signed release artifacts, and controlled lifecycle updates.
02 / ENGINEERING FOCUS
SOC 2-aligned
engineering.
Build for identity and access controls, change management, security monitoring, incident response, and auditable evidence supporting the control environment and audit readiness of a scoped SOC 2 program.
03 / ENGINEERING FOCUS
AI-native Day-2
operations.
Embed AI into application and platform operations to detect anomalies, diagnose issues, plan maintenance, and execute approved runbooks for patching, scaling, recovery, and optimization.
The governed Day-2 operating loop
01
Observe
Collect operational signals
02
Diagnose
Assess issues and context
03
Propose
Prepare a tested runbook
04
Govern
Check policy and approvals
05
Execute
Act within defined limits
06
Verify
Check outcomes and record evidence
Runs continuously — Verify feeds back into Observe
Human governance by design
Autonomous within policy. Accountable to people.
Design low-risk, pre-approved tasks to run automatically within defined limits. Require human approval for high-impact or out-of-policy changes, retain least-privilege access, and record decisions and outcomes. Provide operator stop controls, escalation, and validated rollback or recovery paths.
Intelligence inside your trust boundary.
For air-gapped deployments, keep operational telemetry, models, context, and execution local. Validate runtime dependencies, software imports, and update procedures for the selected environment.
SOC 2 alignment supports audit readiness; it does not, by itself, establish an independent SOC 2 attestation. Autonomous capabilities are validated by the platform, release, and deployment.
Who we are
Builders. Operators.
Long-term partners.
We bring platform developers, architects, and site reliability engineers together around a shared responsibility: building infrastructure that organizations can understand, operate, and trust.
We value technical depth, clear documentation, honest trade-offs, and ownership throughout the system lifecycle. The work is not finished when software is deployed. It continues in how that software is maintained, improved, and supported.
Platform Engineering
Build the software, integrations, and platform experiences that make complex infrastructure usable.
Production Engineering
Bring reliability, observability, operational readiness, and lifecycle discipline into the way platforms run.
Leadership
The people behind the mission.
Get to know the people guiding XaasIO’s strategy, operations, and long-term commitment to critical infrastructure.
Build what the world depends on.
Planning a cloud for government, financial services, pharmaceuticals, healthcare, energy, transport, industry, service-provider operations, or private AI? Work with XaasIO to define the architecture, security boundary, and operating model your environment requires.